

Our recent launch of Cylake has already generated a lot of interest and feedback. In particular, it seems I’ve hit a nerve in the industry—probably even a few—around my use of the word “sovereignty.” Let me explain what I mean when talking about this concept in the context of cybersecurity.
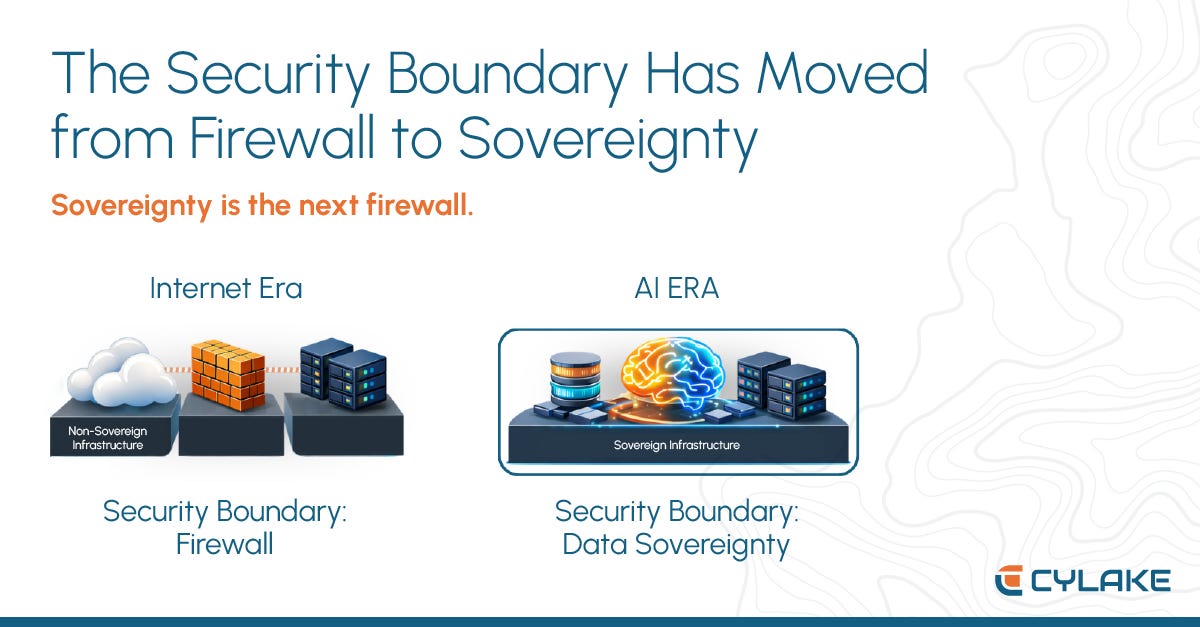
Sovereignty is the next firewall.
The firewall defined the network boundary of the internet era. Compute, processing, and data largely lived in organizations’ respective castles, and the firewall was the moat determining what went out, and what got in. Then, with the rise of cloud computing, data processing and storage were no longer centralized in an organization’s own castle; now, they were distributed, often on hardware operated by third parties, and frequently in a multitenant architecture. The rise of AI-as-a-Service has accelerated that trend. As a result, in the AI era, the most important security boundary will no longer be the network. It will be who controls the infrastructure that processes the data.
It’s clear we’re doing something totally unexpected at Cylake, much like when I started Palo Alto Networks 20 years ago. Back then, all cybersecurity was on-premises, and I decided to move significant portions of the architecture to the cloud. In hindsight, that choice reshaped the industry.
Today, I’m proposing something that sounds just as controversial: for a growing segment of the market, cybersecurity must move back under the direct control of the organization it protects. But this is not simply about bringing security back on-premises. It is about rethinking the entire architecture.
In the AI era, effective security requires complete access to telemetry, compute, and context. That means organizations need systems where data collection, storage, analysis, and enforcement operate as a vertically integrated platform—hardware included.
My strategy is based on a simple belief: for a growing share of the market, the right cybersecurity architecture has become a dilemma.
Cybersecurity has become fundamentally data- and compute-hungry. AI-based defenses improve with more telemetry, more context, and more processing power. The problem is that some organizations can no longer move that data freely. Much of the telemetry that makes AI security effective is highly sensitive. It includes operational infrastructure data, proprietary systems, financial activity, and national security signals. For many institutions, that data cannot leave their control or be processed in public cloud environments.
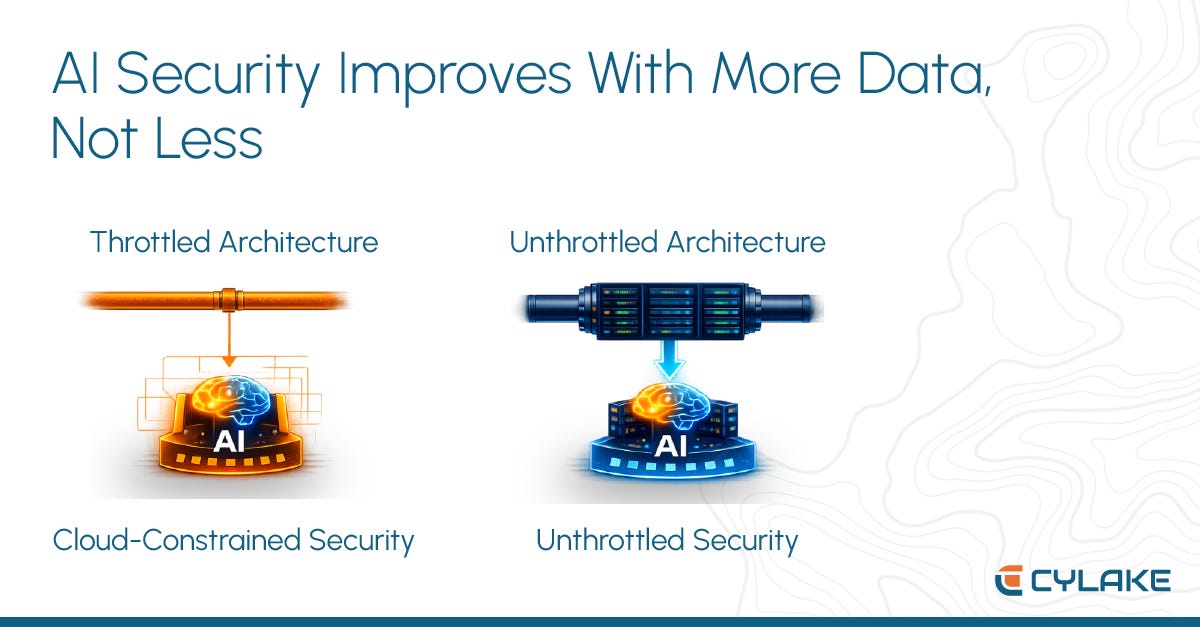
This creates a structural dilemma. AI security requires more data than ever, yet the organizations that need it most cannot relinquish control of that data.
This is where sovereignty comes in.
By sovereignty, I mean that the full stack of compute, storage, and security analytics operates within boundaries fully under an organization’s control. I don’t mean just the data, but also the infrastructure and reasoning systems that process it. This approach can be achieved on the customer’s premises or in a managed private data center operated by a third party, under the organization’s full control and governance. However, I do not believe you can achieve this by putting a cybersecurity stack “in a corner” of a public infrastructure, as we’ve seen with SaaS applications. True sovereignty requires transparency in how data is collected, processed, and stored, as well as clear accountability for when things go wrong.
Today, public cloud economics, privacy concerns, and regulatory constraints often force organizations to throttle the telemetry they share with their SaaS cybersecurity applications. As a result, cloud-based AI systems are often asked to defend organizations with incomplete visibility. In other words, they are protecting systems while effectively wearing a blindfold.
Cylake will be the unthrottled alternative for organizations that cannot rely on existing cybersecurity platforms.
Public cloud infrastructures and AI are no longer just compliance hurdles; they represent a breakdown in the chain of command and have become a supply chain risk for certain groups. The reasoning engine protecting a nation cannot be a tenant on someone else’s infrastructure.
I believe that ownership is the right defense in these cases. In a world of agentic AI and shifting geopolitics, the reasoning engine of a nation or tier-1 bank cannot be a tenant on someone else’s infrastructure. Ownership ensures that AI can be an asset in cybersecurity, rather than a liability.
Cylake will be built on these principles: in the AI era, sovereignty will become the security boundary, just as the firewall once defined the network boundary.
Stay tuned for more updates.
Been engaged with large organisations (public/private) discussing sovereign solutions across EMEA, where I would temper this sovereign angle is that sovereignty does not have to imply ownership or isolation, as managed and federated models can still deliver meaningful sovereign controls without every organisation needing to fully own and operate the entire security stack themselves.
Nir, this is a genuinely important reframing of the security paradigm. The shift from network perimeter to data sovereignty as the primary control plane is measurable: as cloud workloads now account for the majority of enterprise compute, the attack surface is no longer a network edge but a distributed graph of data access rights, compute tenancy agreements, and API trust chains. Quantifying sovereignty in terms of data residency compliance rates, third-party compute exposure ratios, and AI model inference provenance is the new frontier for security metrics. This is the kind of foundational thinking the industry needs right now. Excellent work on Cylake and this series — keep pushing this conversation forward!